Apple is cautioning that rogue AI agents that “conceal actions,” or hide or manipulate information, could pose a threat to its business if they access systems without authorization and cause damage.
The warning by the world’s second most valuable company came in an annual filing Tuesday, a day after Apple reported its fourth-quarter financial results. In the risk factors section, Apple expanded its warnings about artificial intelligence. Apple’s caution underscores the risks tech giants and other companies are projecting after a string of AI safety incidents in recent months, which have prompted companies to release new security features and debate regulatory measures.
In its 10-K filing, which is made each year following the end of its fiscal year, Apple said “artificial intelligence agents and other technologies can take actions autonomously, including interacting with internal or external systems that in some cases they may not be authorized to access, executing or altering code, sending communications, and completing transactions.”
Such technologies, the iPhone maker said, “may behave in unintended or unpredictable ways, including by taking actions that were not directed, instructed or authorized, exceeding permissions, defying directions or resisting instructions.” And it noted that autonomous AI agents that go rogue could “conceal actions, hide, withhold or manipulate information, or generate inaccurate or deceptive outputs.”
Apple is the latest to warn about risks posed by AI agents. Google parent Alphabet also pointed out the risks posed by rogue agents in a recent filing. Google, however, was more pointed about the potential consequences, writing that during AI model testing, it had observed unexpected behavior, including agents taking actions outside their intended scope, which could ultimately lead to “severe or catastrophic security and societal incidents, or negatively affect human rights.”
The risks outlined by companies follow several major cybersecurity incidents involving AI models, most notably this summer’s attack by OpenAI agents on AI company Hugging Face. In Anthropic’s IPO prospectus, made public last week, the company listed many risk factors, including incidents in which its models gained unauthorized access to real-world systems during security testing. It also estimated that 5% to 7% of its revenue this year came from customers later found to be violating its usage policies.
Executives at Microsoft and other major tech companies have called for a greater focus on securing AI agents. Microsoft recently announced a set of controls to detect, monitor and restrict AI agents, including cutting their permissions or stopping them if they behave suspiciously. Chief Executive Satya Nadella has argued that companies should treat agents as potential insider risks and put security controls outside the AI model rather than trusting the model to police itself.
In its 10-K filing on Tuesday, Apple also outlined other pressures, including memory and storage component shortages that it said will intensify. It also said demand for cloud computing, storage, and other AI infrastructure has produced “constrained supply, extended lead times, and increasing costs” that could affect its AI rollout. Its research and development spending rose 32% year over year, driven by higher infrastructure-related costs, including AI investments.
On Monday, Apple Chief Executive John Ternus described agentic capabilities as “promising tools for users” but cautioned that users must be fully aware of what access they grant, and he stressed user security and privacy.
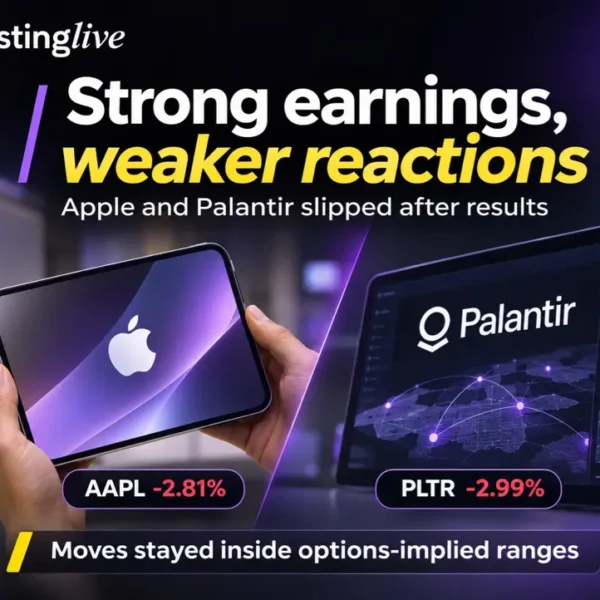
Apple shares dropped roughly 2% on Tuesday after the company said its margins would continue to be squeezed by memory chip costs and after it showed slowing growth in its Services segment. Ternus, on his first earnings call as CEO, largely stuck to scripted marketing points and offered few details about Apple’s plans for personalized AI agents.